The Ultimate Guide to Security Operations Centres
A curated Kiwi edition of IndustrialDay news, analysis, interviews, reviews, job moves, and related resources for Security Operations Centres (SOCs).
What to know about Security Operations Centres
A Security Operations Centre (SOC) serves as the critical hub for monitoring, detecting, and responding to cybersecurity threats within organisations. Covering a wide spectrum of digital environments, SOCs integrate advanced technologies such as AI, machine learning, and automation tools to enhance threat detection and incident response capabilities.
Exploring recent developments in this field reveals insights on evolving challenges like alert fatigue, skills shortages, and the increasing complexity of cyberattack surfaces. Readers can learn how organisations leverage innovations in SOC-as-a-Service, AI-driven threat hunting, and next-generation platforms to build adaptable, efficient security operations tailored to their needs.
Whether you are an IT professional, security analyst, or business leader, following stories under the 'Security Operations Centre' tag offers valuable perspectives on managing cyber risk, improving operational efficiency, and preparing your organisation for the dynamic cybersecurity landscape ahead.
Kiwi Security Operations Centres News
Regional stories with direct local relevance
SSS launches managed security service in New Zealand
Public bodies and mid-market firms in New Zealand can now use a single managed cyber service to cut tool sprawl and relieve overstretched IT teams.
Securecom appoints Head of Cyber Security & promotes Kolver
Sharp New Zealand's backing is accelerating Securecom's growth as it adds senior cyber expertise and broadens product and commercial leadership.
iSANZ finalists highlight New Zealand cyber sector shift
Finalists span corporates, councils and start-ups as New Zealand's cyber work shifts towards resilience, behaviour and AI, iSANZ says.
QuizFlight adds knowledge tags to security training
Security teams can now pinpoint training gaps by topic as QuizFlight's tagging system measures understanding, not just course completion.
Spectrum partners with Arctic Wolf on cyber services
New Zealand firms can now outsource 24x7 threat monitoring as Spectrum adds Arctic Wolf's managed detection and response to its resilience stack.

From biometrics to zero trust secures physical-digital divide
Organisations are pairing biometrics with layered access controls as cyber and physical threats converge inside data centres and other sensitive facilities.
Analyst Insights
Research and market analysis connected to Security Operations Centres
Contrast Security named leader in IDC DAST assessment
Hack The Box launches AI range for enterprise security teams
Airrived named leader in IDC MarketScape for AI SOC
DigiCert launches Quantum Central for post-quantum shift
DigiCert sees demand for certificate automation surge
Featured News
AI demands network agility and better operational governance
Governance gaps are leaving most organisations exposed as AI traffic surges and networks struggle to keep pace with machine-speed demands.
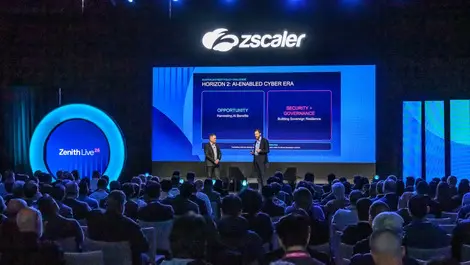
Zscaler takes zero trust beyond the corporate network
Critical infrastructure operators are using cellular links to secure distributed assets as outages and spoofing raise the stakes for resilience.
Filigran: Does your CISO know enough?
CISOs are under pressure to answer boardroom questions on exposure in minutes, as Filigran pushes CTEM and open-source validation tools.
AI transforming physical security into enterprise data solution
AI and cloud tools are turning cameras into live operational data sources, helping firms cut costs, spot errors and manage fleets centrally.
Mimecast CEO: Agentic AI threat novel but not entirely new
Hidden AI risks are already widespread in workplaces, with Mimecast saying users are driving shadow tools and most exposure still starts with people.
Trusted identity cuts across physical and logical systems
Unified identity systems can cut admin overhead and shrink attack surfaces as remote work and cyber threats blur physical and digital access.
Apple's Unified Memory powers Kiraa AI's rapid automation
Australian firms can speed month-end processing from days to an hour by running Kiraa AI on Macs instead of costly cloud servers.
AI models expose new attack surfaces through misconfiguration
Misconfigured models are giving attackers a fresh route into cloud systems, raising the risk of data theft and service compromise.
Reviews
Expert Columns
Seven Cyber Controls Businesses Can No Longer Afford to Overlook
Integrated video security - a must for modern preschools
In the AI era, channel value is being redefined
Cybersecurity finds problems. AI can accelerate remediation
Cybersecurity is operating on the wrong clock
The autonomous SOC takeover

How security leaders should measure AI SOC performance
AI closes vulnerability window as zero-day exploits surge
Collective cyber defence will be won or lost in how we act together
Machine vs. machine: The new reality of cybersecurity in ANZ
Interviews
Interviews and video coverage from the networkRecent Security Operations Centres News
Arctic Wolf says AI resolves 60% of security cases
Arctic Wolf says AI now resolves 60% of security investigations, while monthly investigation volumes rise and alert volumes fall across more than 11,000 organisations.
Proofpoint joins Microsoft ICES in Defender portal
Microsoft 365 customers can now review Proofpoint email threat alerts inside Defender, cutting the need to switch between security tools.
Cisco warns Singapore firms struggle to spot compromised AI
Just 38% of Singapore organisations feel able to detect and respond to compromised AI agents, as 89% suffered a cyber incident last year.
Most DLP tools catch data loss only after exfiltration
Only 16% of respondents said their most significant data loss incident was blocked before data left, highlighting gaps in DLP controls as AI use grows.
Sumo Logic previews Root Cause Agent for DevOps teams
The new tool is aimed at cutting incident triage from hours to minutes by analysing logs and metrics for likely causes automatically.
Sygnia opens AI security hubs in Austin & Singapore
The move will let customers get round-the-clock monitoring as Sygnia widens its follow-the-sun cyber security coverage across three regions.
Graylog launches AI case system in security platform
Security teams may cut alert overload as Graylog's new case system groups evidence and lets AI triage incidents before analysts step in.
Acronis adds dark web monitoring to MDR service
Managed service providers can now spot exposed credentials and leaked data more quickly, with Acronis also widening multilingual support and customer alerts.
Securonix launches behavioural analytics for AI threats
With AI agents widening the attack surface, security teams need to spot abnormal activity across human and machine users before damage is done.
Qualys warns patching surge is missing active exploits
Despite more patching, organisations are leaving the most dangerous flaws open longer, as attackers exploit vulnerabilities before defenders can act.
TrendAI adds NVIDIA Nemotron to sovereign security cloud
The move lets regulated organisations run AI-driven threat detection inside customer-controlled environments, keeping sensitive security data local.
Palo Alto warns on 22 million exposed PHP instances
Security teams face a wider attack surface, as Palo Alto Networks says the PHP flaws could leave 22 million internet-facing instances exposed worldwide.
SentinelOne names LevelBlue global Wayfinder partner
More organisations will gain round-the-clock threat detection and incident response as LevelBlue takes global delivery of SentinelOne's Wayfinder service.
Gigamon launches GigaVUE-GSA110 for AI network ops
As AI workloads spread across cloud and on-premises systems, network teams need more context to spot shadow AI and govern traffic.
Tenable launches open AI partner network for security
Security teams can now connect exposure data with third-party AI tools to triage risks faster without building custom integrations.
Arctic Wolf launches AI oversight tools for security teams
Security teams are being offered earlier attack interruption and clearer AI decision trails as the company adds three products to its Aurora platform.
Most EMEA & Asia Pacific firms lack mature security ops
Nearly two-thirds of organisations are still exposed to fast-moving cyber attacks because they lack round-the-clock security operations and automation.
Tanium relaunches Security Operations to counter AI attacks
The update aims to help security teams spot and stop AI-driven intrusions that use stolen credentials and trusted tools rather than malware.
Netskope launches AgentSkope marketplace for teams
The new marketplace lets customers manage AI agents in one console, easing procurement bottlenecks and helping overstretched security teams triage alerts faster.
Tanium relaunches security platform to counter AI attacks
The update aims to help security teams spot intrusions that use stolen logins and normal admin tools, which can evade signature-based defences.